

Fixes and safety
Safety model
Your own team performs the last write to your estate. This is what has to happen before they are asked to.
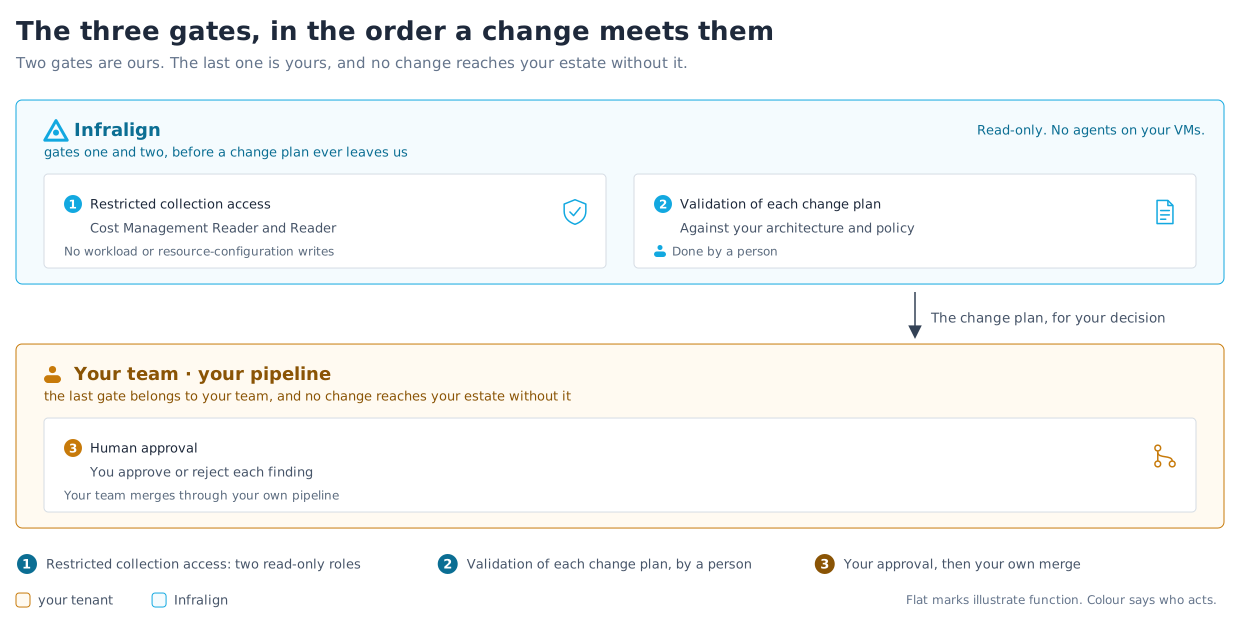
Infralign writes nothing to your Azure estate. Three gates stand between a finding and a change. Your team’s approval is the last. Figure 1 shows them in the order a change meets them.
Gate one: restricted collection access
Section titled “Gate one: restricted collection access”Dashboards, reports, chatbot and audit all read through read-only roles:
- Infralign reads through a service principal in your own tenant, holding two roles by default: Cost Management Reader and Reader. A third, Storage Blob Data Reader on the export container, is added only if you opt into the FOCUS export lane. Scopes are in the permissions reference, and setup is in connect Azure.
- The nightly run is pull-based. No agents or extensions are installed on your VMs, and no standing production privilege exists.
- Access is revocable without action from Infralign: remove every role assignment held by the Infralign application at your scope, then disable or delete the application, and collection stops within about 10 minutes. The role list, the reason the order matters, and the timing bound are in ending the connection, which owns that procedure.
The permissions reference lists every action the two roles cover.
Gate two: validation
Section titled “Gate two: validation”Before an approved fix becomes a change your team merges:
- Each change plan is checked against your architecture and policy constraints. A change that saves money by degrading reliability or security posture is reworked or dropped.
- Findings carry their utilisation evidence and confidence levels: 30-day p95 CPU, and idle-days. Every finding rests on how the resource is actually used.
- Blast radius, and any app code changes, are made explicit before review.
Gate three: human approval
Section titled “Gate three: human approval”Nothing changes without a human decision. You approve or reject each finding in the app, and approved changes are merged by your own team through your own pipeline, under your own controls. Infralign’s involvement ends at the approved change plan.
Isolation and access controls
Section titled “Isolation and access controls”Beyond the three gates, the application is scoped to your own tenant: a dedicated warehouse with no cross-tenant query path, a chatbot allowlisted to your own tables, and a sign-in allowlist bound to your tenant ID. Isolation and data handling owns all three.
Where this model comes from
Section titled “Where this model comes from”This is the same review-gated model used in the founding engagements, where it produced €750K a year of recurring saving with no production outage from an approved refactor.
Gate one is the two read-only roles. Permissions gives their exact scopes. Ending the connection is how you take them back.